01 / TEST
Penetration
testing.
Understand what an attacker could exploit — and what your team should fix first.
Book a 30-minute call01 / THE STARTING POINT
Put your defences
to the test.
A product launch, a customer security review, or a major change to your systems can all raise the same question: where are we exposed?
We agree the systems, access and testing boundaries with you, then investigate exploitable weaknesses within that scope. The focus is on evidence your engineers can act on.
What we can cover
- External infrastructure — internet-facing systems and services
- Web applications and APIs — authentication, access control and business logic
- Internal networks — access paths, privilege escalation and segmentation
- Cloud environments — identities, permissions and exploitable configuration weaknesses
Each engagement covers the agreed testing type, targets and depth. Testing types can be combined where required; scope, timing and fees are confirmed before work begins.
02 / WHAT YOU GET
Findings you can
work with.
Validated findings
Reproduction steps and supporting evidence, with affected assets and the conditions needed to exploit each weakness.
A clear order of action
Technical severity alongside business context, so your team can prioritise remediation and understand the trade-offs.
Practical remediation guidance
A report and a findings walkthrough with your team. We agree whether a retest is needed and include it in the scope.
A LOOK INSIDE THE REPORT
See what
you’ll receive.
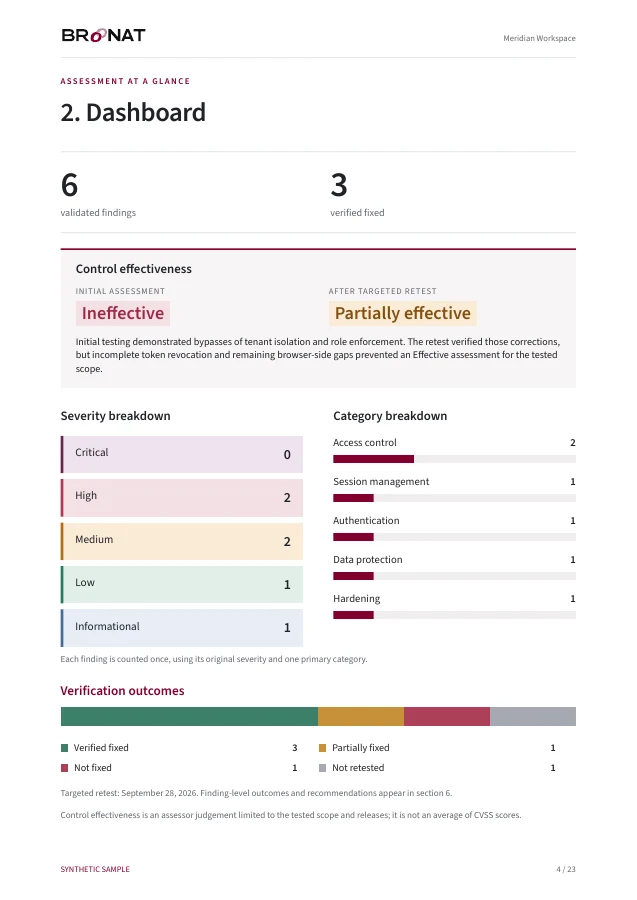
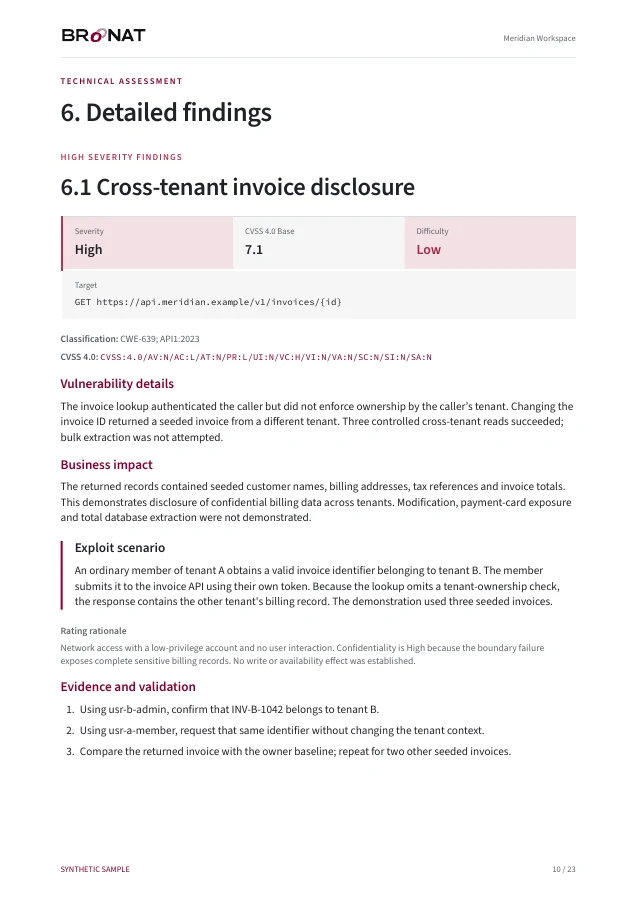
Explore an illustrative web application and API penetration test report: business context, validated findings, technical evidence and practical remediation guidance.
Synthetic sample · Fictional client, systems, identities and evidence. The example includes retest outcomes; retesting for your engagement is agreed in scope.
03 / WORKING TOGETHER
Clear scope.
Shared expectations.
Scope & authorise
Agree targets, access, testing windows, rules of engagement and a point of contact.
Test & validate
Investigate weaknesses and validate their impact. Escalate urgent findings through the agreed channel.
Explain & prioritise
Walk through the findings, remediation options and any follow-up testing.
A penetration test is a point-in-time assessment of an agreed scope. It cannot establish that a system has no vulnerabilities.
YOUR NEXT MOVE
What needs a
closer look?
Bring your application, infrastructure, cloud environment or deadline. We’ll start by understanding the scope.
Book a 30-minute callScope, timing and fees agreed before work begins.